Information Security
We Embrace
Core Data Privacy and
Security Regulations
At Osiz Technologies, protecting your data is our highest priority. We adhere strictly to the requirements of global security frameworks and data privacy regulations to ensure your information remains safe and compliant.
ISO 27000 Family: Ensuring your data is shielded with the highest level of care through our Information Security Management System (ISMS).
ISO 9001:2015: Guaranteeing that our quality management processes meet top-tier international standards.
NIST 800 Family: Aligning our software development framework with benchmark security requirements for the Software Development Life Cycle (SDLC).
GDPR: Fortifying data privacy and security for our clients operating within or serving the European Union.
HIPAA & PCI-DSS: Ensuring strict compliance for healthcare and financial technology projects, protecting sensitive patient records and payment information.
CCPA: Assuring the same rigorous level of data privacy and security for our US-based clients.
Our Full-Fledged InfoSec Approach Spreads Across
Five Dimensions
Our working model is designed to be secure, trustworthy, and resilient. From proactive threat monitoring to robust infrastructure and an unwavering focus on intellectual property protection, we are setting the standard for enterprise-grade safety.
Secure Infrastructure
We maintain a robust hybrid infrastructure across our global offices and secure data centers in India and Canada. This setup allows us to process client data securely within localized boundaries. Our infrastructure is fortified across multiple layers:
Physical: Gated and secured buildings with 24/7 video monitoring and personalized access control.
Network: Advanced firewalls, Intrusion Detection Systems (IDS), and strict BYOD policies for our remote teams.
Application: State-of-the-art antivirus, encryption software, and Identity and Access Management (IAM) systems.
Data: Secure, restricted-access repositories ensuring high-level security standards for all client assets.
Secure Software Development Life Cycle (SDLC)
Our product delivery process is built according to Zero Trust principles, which imply clearly stated requirements for the software development process:
Secure Coding Practices: Implementing code obfuscation and strict architecture requirements.
Multi-layer Quality Assurance: Integrating automated testing and peer reviews.
Vulnerability Management: Continuous vulnerability reporting and rapid response programs.
Version Control: A 100% version control process with 24/7 monitoring and logging on all stages of development.
Third-Party Risk Management: Clear policies for third-party contracts to mitigate external risks.
Personal Data Protection
Secure communication is standard from the moment you engage with Osiz. We operate software that aligns with GDPR and CCPA standards, running regular internal audits, monitoring security events, and logging all actions on information assets. Our data protection strategy includes:
Access Control: Strict user activity control and segregation of duties.
Data Encryption: End-to-end encryption for data in transit and at rest.
Anonymization: Pseudonymisation and anonymisation techniques to protect user identities.
Recoverability: Comprehensive backup and data destruction policies.
Information Security Procedures (ISP)
Our rules, expectations, and overall information security strategy are well-articulated, documented, and updated in our ISP guidelines. This involves identifying possible risks, conducting 100% assessments of systems and processes, and training our 400+ dedicated engineers on security best practices on a regular basis.
Intellectual Property Protection
When crafting our infrastructure, we integrate the expertise of vetted solution architects and legal advisors to manage the intricacies of working with clients' intellectual property. With strict Intellectual Property Protection (IPP) policies in place, we guarantee that your proprietary code, algorithms, and business logic remain safe and sound within our infrastructure.
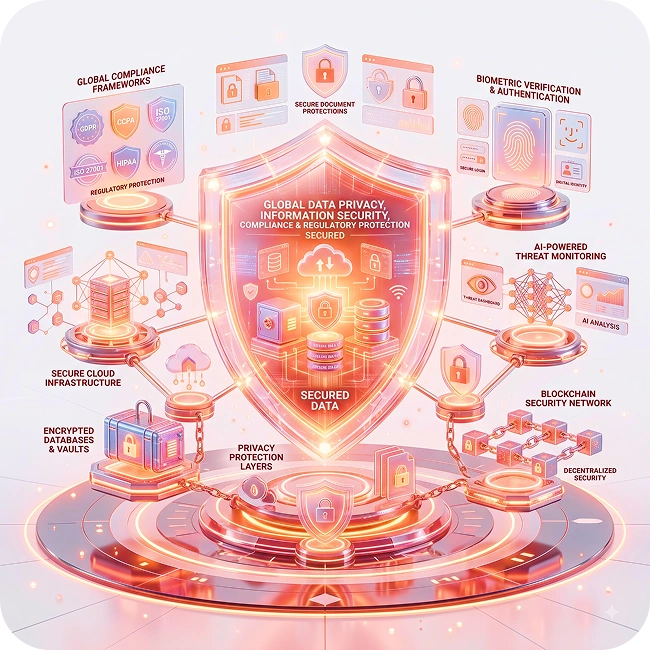
We Run Regular Internal Audits and Security Exams
Osiz Technologies conducts annual internal audits of IT systems, security documentation, and information assets in accordance with ISO 27001 standards.
We maintain a comprehensive Incident Response Plan (IRP) to tackle any security issues effectively. If a security anomaly occurs, our team performs an emergency audit to instantly spot the problem and mitigate its negative impact. Furthermore, our comprehensive policies are supported by ongoing staff training. To minimize the probability of human error, we conduct security awareness training for new staff members, and every employee undergoes annual security knowledge tests.
Advanced Cybersecurity Solutions for Modern Enterprises
Going beyond basic infrastructure security, Osiz provides specialized, AI-powered cybersecurity solutions tailored to your specific industry needs:
Meet the Six Vital Components of Our Benchmark Security Model
Treating security as our top business priority has led to the development of the Osiz InfoSec framework. We ensure the integrity and reliability of your information through six core components:

Confidentiality
Our internal infrastructure is designed as a secure closed network with strict access rules, available only for authorized users.

Non-repudiation
Every single action within our internal infrastructure is logged and tracked, ensuring complete transparency.

Accountability
Every member of our team who interacts with your proprietary data is automatically a responsible person for the security of those assets.

Authenticity
No one can access Osiz infrastructure without passing through rigorous identity checks and corporate credential systems.

Integrity
We implement stringent measures against both intentional and inadvertent alterations to system and personal data.

Availability
We prepare backup and data recovery plans for every system, supported by high-availability internet connections with automatic failover to ensure uninterrupted service delivery.
Safe Data Transfer is a Given
Beyond the explicit details of our certifications lies the nuanced concern of data security during transfer between our infrastructures. Osiz Technologies highlights all shadow areas to avoid misunderstandings. We capture clear agreements on shared responsibility for secure data transfer in our contracts, guaranteeing that your personal information and proprietary data are protected with a secure transfer shield at all times.
Partner with an Enterprise-Grade Security Provider
Whether you are operating in Finance, Healthcare, Retail, Government, or Telecommunications, Osiz Technologies provides reliable, cutting-edge cybersecurity to keep your business safe. Let us handle the complexities of digital defense so you can focus on driving your innovation forward.


No 22,Astalakshmi Nagar, Thanakankullam, (Opp Seetha lakshmi Mill gate Bus stop) Thirunagar, Madurai - 625 006.
(Corporate Office)


Canada Office address, 1150, Rue Patrick, Laval, Quebec - H7Y 2C4, Canada.
(Sales Office)


Explore
Our AI Portfolio

 Artificial Intelligence
- AI Development
- AI Predictive Analytics Services
- AI SaaS Development
- RAG Development
- AI Assistant Development
- ChatGPT Development
- Data Analytics Services
- AI Copilot Development
- Adaptive AI Development
- Machine Learning Development
- NLP
- AI Consulting Services
- AI Software Builder
- AI Token Development
- AI Integration Services
- Enterprise AI Solution
- AI As a Service
- AI Marketing Tools
- AI Video Generator
- Computer Vision Services
- Explore AI
- Dataset
- Machine Learning in Healthcare
- Machine Learning in Retail
- Hire AI Engineers
- Hire Prompt Engineers
- Hire ChatGPT Developers
- Hire Stable Diffusion Developers
- Hire Action Transformer Developers
- Blockchain
- Blockchain Development
- Private Blockchain Development
- Smart Contract Development
- Custom Blockchain Development
- Solana Blockchain Development
- Polygon Blockchain Development
- Public Blockchain Development
- DAO Blockchain Development
- Binance Smart Chain (BSC) Blockchain Development
- DApp Development
- Solana DApp Development
- White Label Blockchain Solutions
- Custom Blockchain On Avalanche
- Custom Blockchain On Polygon
- Blockchain Game Development
- Blockchain Consulting Services
- Blockchain Explorer Development
- Ethereum Blockchain Development
- TRON Blockchain Development
- Prediction Market Platform Development Company
Layer 1 & 2 Solutions- Layer-1 Blockchain Development
- Cross Chain Bridge Development
- Data Availability Layer Development
- Ethereum Layer 2 Scaling Solutions
- Cross-L2 DEX Solution
- Layer 2 Token Development
- Layer 2 Token Marketing
- Layer 2 Cryptocurrency Development
- Layer 2 Solutions For Blockchain Games
- Layer 2 Solutions For Web3 Gaming
- Layer 2 Blockchain Solutions
- Rollups As A Service
- Optimistic Rollups Development
- ZK Tech Development
- Bitcoin Layer 2 Solutions
Crypto Exchange- Cryptocurrency Exchange Development
- White Label Crypto Exchange
- Decentralized Exchange Development
- P2P Exchange Development
- Crypto Derivatives Exchange Development
- Centralized Exchange Development
- Crypto Exchange Clone Script
- Cryptocurrency Exchange App Development
- OTC Exchange Development
- Exchange Listing Services
- Binance Like Exchange Development
- Bitstamp Like Exchange Development
- Crypto Exchange Script
CryptoCrypto WalletToken Standards- Token Development
- AI Token Development
- RWA Tokenization Development
- Coinremitter Clone Script
- Asset Tokenization
- Real Estate Tokenization
- Tokenization Platform Development
- Crypto ETF Development
- Solona Token Development
- Semi-Fungible Token Development
- BEP20 Token Development
- Ethereum Token Development
- ERC1400 Token Development
- ERC998 Token Development
- ERC 721 Token Development
- ERC20 Token Development
- Defi Token Development
- ERC1155 Token Development
- BEP721 Token Development
- Utility Token Development
- ERC 777 Token Development
- ERC 827 Token Development
- Social Token Development
- Metaverse Token Development
- Tron Token Development
- ERC404 Token Development
- Governance Token
- Shibarium Token
- polygon Token
- BRC-20
- TRC20 Token Development
- TRC10 Token Development
- Soulbound Token Development
- NFT Token Development
Trading BotsClone- Crypto Exchange Clone Script
- Binance Clone Script
- Metamask Clone Script
- Coinbase Clone Script
- Kucoin Clone Script
- Paxful Clone Script
- Remitano Clone Script
- Wazirx Clone Script
- ByBit Clone Script
- Bitfinex Clone Script
- MEXC Clone Script
- Bitget Clone Script
- Cointool App Clone Script
- Trust Wallet Clone App
- Coinmarketcap Clone Script
- Changelly Clone Script
- BingX Clone Script
CybersecurityApp SecurityDigital Forensics & Incident ResponseAudit & ConsultingEducation & TrainingSolutionsWeb 3DeFi- Decentralized Finance (DeFi) Development
- DeFi Lending/ Borrowing Platform Development
- DeFi Staking Platform Development
- DeFi Token Development
- DeFi Wallet Development
- DeFi Smart Contract Development
- DeFi DApp Development
- Decentralized Exchange Development
- DeFi Insurance Development
- DeFi Crypto Synthetic Assets Development
Game Development- Game Development
- Android Game Development
- IOS Game Development
- Metaverse Game Development
- VR Game Development
- AI Game Development
- Unity 3D Game Development
- Unreal Engine Game Development
- Mobile Game Development
- Blockchain Game Development
- NFT Game Development
- Play to Earn Game Development
- Move to Earn Game Development
- Casino Game Development
- Slot Game Development
- Poker Game Development
- AAA Game Development
- AR Game Development
- Social Network Game Development
- Gamification Services
- Decentralized Sports Betting Platform
- Sports Betting Dapp Development
- Blockchain Casino Game Development
- Game Asset Creation
- Baccarat Game Development
- Rollbit Clone Script
- Fortnite Clone Script
- Slot Game Development
- Tap to Earn Game Development
- Slot Game Development
Metaverse Platforms- Metaverse Game Development
- Metaverse Event Platform Development
- Metaverse Virtual Mall Development
- Metaverse NFT Marketplace Development
- Metaverse Token Development
- Metaverse Virtual Land Development
- Metaverse Avatar Development
- Metaverse 3d Space Development
- Metaverse Real Estate Development
- Metaverse Social Media Platform Development
- Top 10 Metaverse Development Company
- Metaverse Business Ideas
- Metaverse Launchpad Development
- Metaverse App Development
- Metaverse Casino Game Development
NFT SolutionsNFT Platforms- NFT Minting Development
- NFT Token Development
- NFT Exchange Platform Development
- NFT Launchpad Development
- NFT Fashion Marketplace Development
- NFT Art Marketplace Development
- NFT Music Marketplace Development
- Carbon Credits NFT Marketplace Development
- Binance NFT Marketplace Development
- Polygon NFT Marketplace Development
- Solana NFT Marketplace Development
- Influencers NFT Marketplace Development
- NFT Ticketing Marketplace Development
- DeFi NFT Marketplace Development
- NFT Fantasy Sports Platform Development
- NFT Storage Development
- NFT Lending Platform Development
- Top10 NFT Business Ideas
NFT Game ClonesSustainabilityServiceNow - Blog
- Contact Us
- Works